Establish the surface and scope.
Identify the endpoint, its owner and the specifications or connection details needed for supported checks. Keep the authorised scope clear before testing.
Bring web and API surfaces, test coverage and findings into the product view. Review authentication, configuration and application behaviour within an authorised testing scope.
01Which surfaces belong to us?
02Which have been tested?
03What does the finding mean for the product?
Bring the resource, finding and product relationship into one useful conversation.
Identify the endpoint, its owner and the specifications or connection details needed for supported checks. Keep the authorised scope clear before testing.
Use supported web and API checks to investigate the agreed surface. Keep test evidence, the technical finding and its product context together.
See which endpoints were tested, when they were tested, and where evidence is still missing. An untested surface stays visible as a gap.
Connect the interface a user reaches to the service, workload and product behind it. Investigate exposure with the context needed to act.
Explore the platform ↗Available checks depend on the resource, integration and agreed assessment scope.
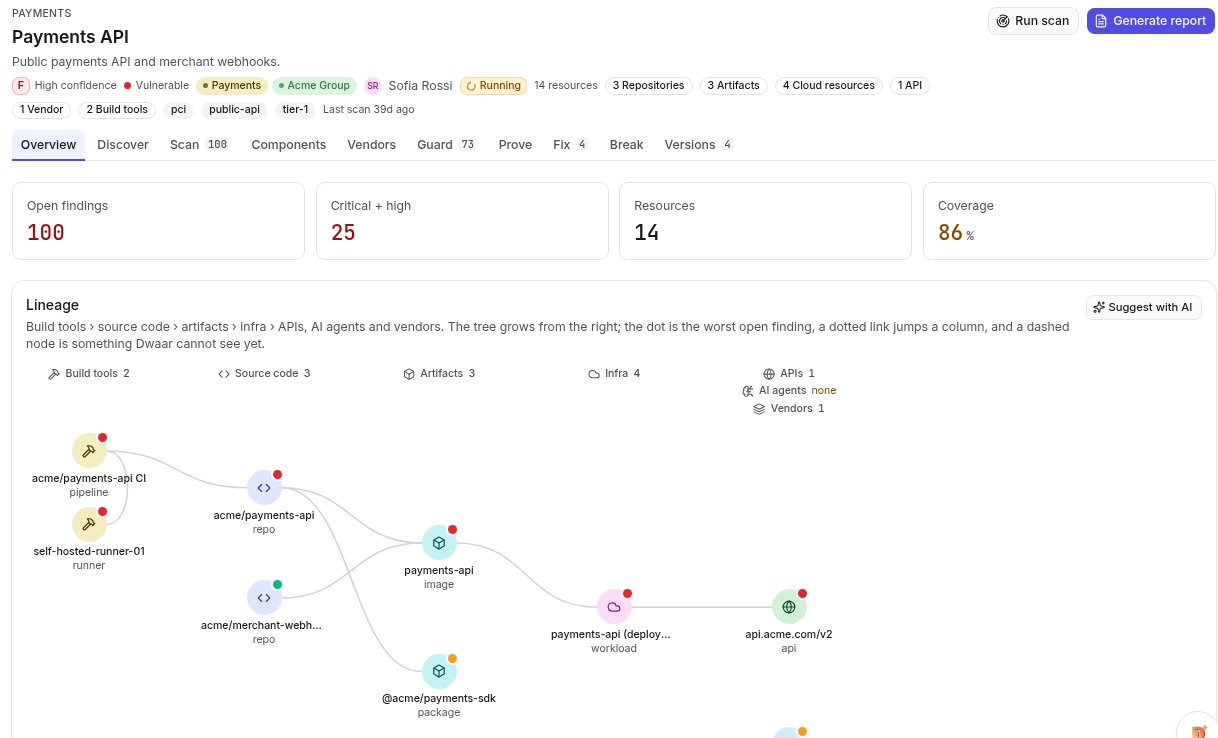
Review the product context alongside findings and coverage. Click the capture to inspect it in full.
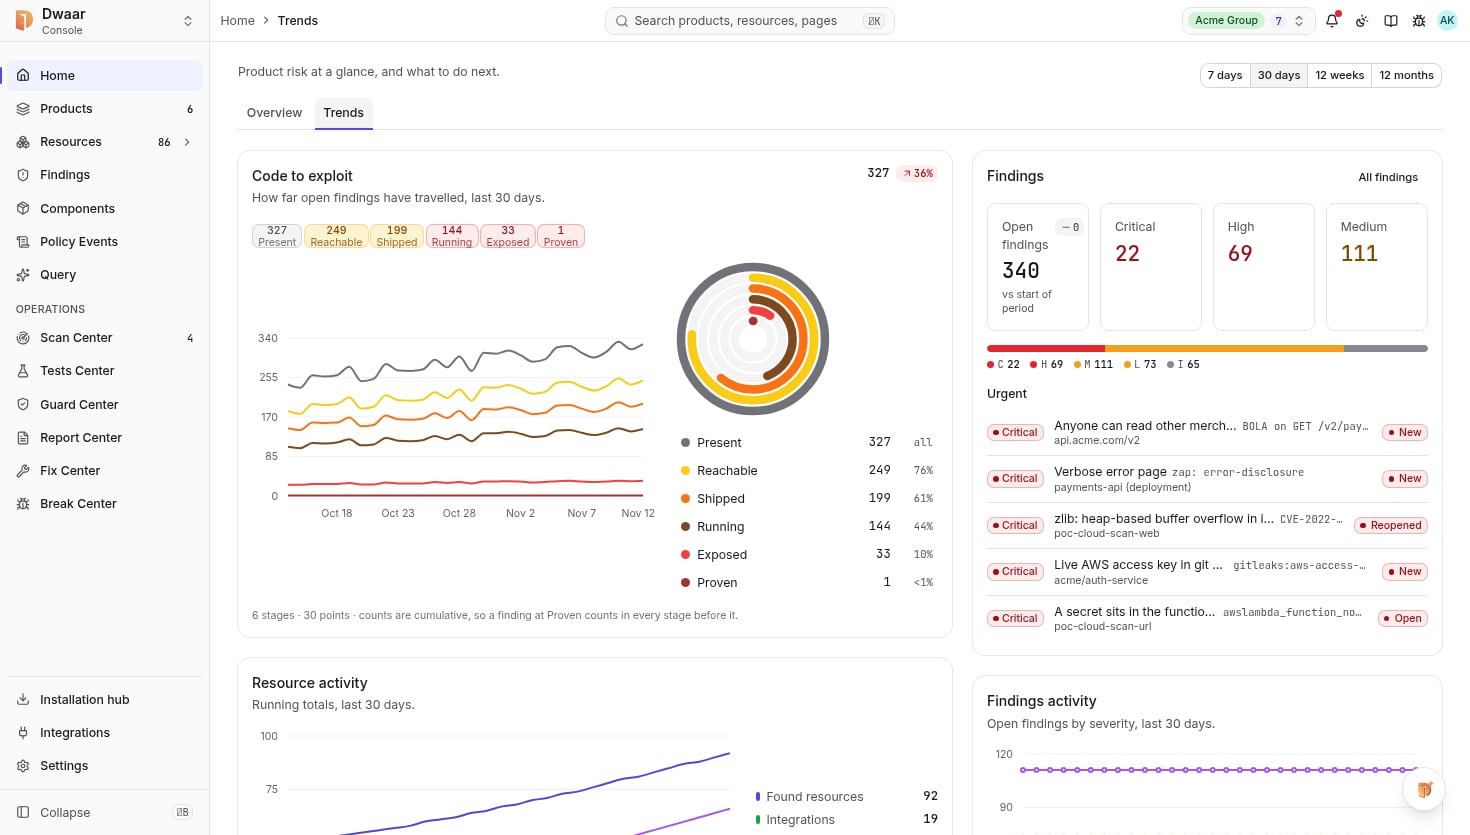
The Dwaar Portal plans and analyses. Live requests to your application are sent by the Dwaar CLI on the machine you control.
Supported connector configuration can describe authentication, sessions, requests and response parsing. The exact testing scope is agreed for your application.
No. Registration, connection validation and a live assessment are distinct steps. Test coverage reflects the assessment evidence available.
Start with one product. Connect the context. Give your team a clear next action.